Published 2026-09-29 · Updated 2026-11-13
Cloudflare's H1 2026 DDoS Report: What a 31.4 Tbps Record Means for a Small Business Server
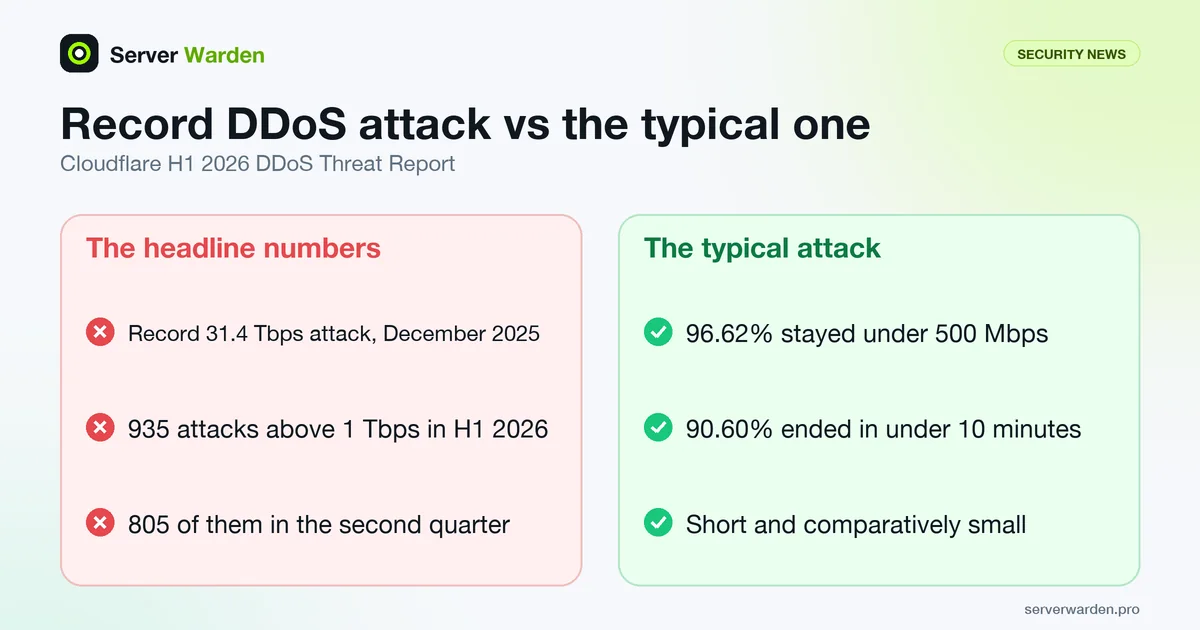
According to Cloudflare's H1 2026 DDoS Threat Report, published 11 August 2026, 96.62% of network-layer DDoS attacks stayed under 500 Mbps and 90.60% ended in under 10 minutes. For a small business server that means the typical attack is short and modest, not a terabit flood. Cloudflare also warns that even a 100 Mbps attack can overwhelm an unprotected server, so protection has to be in place before an attack starts.
The 31.4 Tbps record in the title is not from this report: Cloudflare disclosed it earlier, in its Q4 2025 report. We checked every figure below against Cloudflare's own posts, put them in a table with what each one means for a VPS, and explain what a CDN covers and where it stops.
In this article
Where do the 31.4 Tbps record and the 935 attacks over 1 Tbps come from? Key figures from the report and what they mean for you DDoS terms a beginner meets in the report How big and how long is a typical attack? Can a small attack still take a small server offline? What does a CDN protect, and what does it leave open? Has anything changed since the H1 report? Sources and how this page was checked Frequently asked questionsQuick win (10 minutes)
- Confirm your site sits behind a CDN or reverse proxy rather than exposing the origin server's IP directly.
- From another machine, check that your server does not answer around the CDN:
curl -sSk -m 8 -o /dev/null -w '%{http_code}\n' --resolve example.com:443:203.0.113.10 https://example.com/(use your own domain and server IP). A200means the origin answers directly. - Check current request limits on your web server:
nginx -T | grep limit_reqif you run nginx. - Confirm your firewall has a sensible connection-rate limit on public-facing ports, not just an allow list.
- Check whether fail2ban or an equivalent is watching for repeated connection floods, not just failed logins.
- If you have never tested what your server does under a traffic spike, treat that as the real gap, not the size of the largest attack in the news.
Where do the 31.4 Tbps record and the 935 attacks over 1 Tbps come from?
The 31.4 Tbps record comes from Cloudflare's Q4 2025 report (5 February 2026), which says the attack lasted 35 seconds and was mitigated automatically. Cloudflare's post on its 500 Tbps network capacity (10 April 2026) names the Aisuru-Kimwolf botnet as the source. The H1 2026 report counts 935 network-layer attacks above 1 Tbps, 805 of them in the second quarter.
That leaves about 130 in the first quarter (our arithmetic: 935 minus 805), which fits the report's +519% quarter-over-quarter change. The posts we read give no month for the 31.4 Tbps attack, and none of them break the largest attacks down by victim size.
Key figures from the report and what they mean for you
These are the figures we verified against Cloudflare's text on 13 November 2026. The last column links the post each number comes from. Cloudflare's numbers describe its whole network, so read them as context, not as the odds that your own server is attacked.
| Key figure | Value | What it means for a small business | Source |
|---|---|---|---|
| Network-layer DDoS attacks mitigated, H1 2026 | 23.2 million (about 5,343 per hour) | An average over Cloudflare's whole network, not attacks aimed at small sites. It shows attacks are constant background, not rare events. | H1 2026 |
| HTTP DDoS requests, H1 2026 | 29.64 trillion | These are requests, not attacks. Request floods look like normal visitors, so rate limiting on login, search and API endpoints still matters. | H1 2026 |
| Attacks above 1 Tbps | 935 (805 in Q2, +519% on Q1) | Record scale is growing, but only a network of Cloudflare's size can absorb it. A single origin server cannot. | H1 2026 |
| Network-layer attacks under 500 Mbps | 96.62% | The typical attack is small by Cloudflare's standard, but Cloudflare says 100 Mbps can overwhelm a server or website. | H1 2026 |
| Network-layer attacks ending in under 10 minutes | 90.60% | No time for a human to react. Protection must already be on when the attack starts. | H1 2026 |
| Largest attack Cloudflare disclosed | 31.4 Tbps, 35 seconds, Aisuru-Kimwolf | A sign of what botnets can do. It is not a size to plan your own server around. | Q4 2025 |
| Peak month | April 2026: 6.46 trillion requests, 165 PB | Volume swings by month. Cloudflare says the later decline may reflect Operation PowerOFF, a 21-country action against DDoS-for-hire users, so one month is not a trend. | H1 2026 |
| DNS-based attacks | 34.3% of network-layer attacks; DNS floods 25.7% in Q1, 40.0% in Q2 | Your domain's DNS can be attacked too. If you run your own DNS server, it is a target; a DNS provider with DDoS protection takes that load. | H1 2026 |
| CLDAP floods | +580% on Q1, third most common vector in Q2 | This abuses Active Directory LDAP over UDP port 389. It only touches you if that port is open to the internet, which on a VPS it should not be. | H1 2026 |
| Most attacked industry | Media, Production and Publishing: 14.2% of HTTP DDoS requests in both quarters; Government from #29 to #9 | Targets follow news events (Cloudflare cites Iran, Ukraine, the World Cup). The ranking is a share of requests, not a risk score for your site. | H1 2026 |
| Top source country, H1 | Brazil 14.9%, United States 13.4%, Indonesia #3 | Source countries show where infected devices sit, not who is behind an attack. Blocking a whole country is a weak defense (our assessment). | H1 2026 |
DDoS terms a beginner meets in the report
Five terms carry most of the report. Each is explained here in one sentence, and the glossary has longer entries.
- DDoS attack: many compromised devices, a botnet, send traffic at one target until real visitors cannot get through (DDoS attack).
- Network-layer DDoS: a flood at the network or transport layer (layers 3 and 4), such as UDP floods, SYN floods and DNS amplification, that fills the bandwidth or the connection tables (volumetric attack, protocol attack).
- HTTP DDoS: a flood of web requests that look like normal visitors but arrive in huge numbers, also called an application-layer attack; Cloudflare counts these in requests, not in attacks.
- Hyper-volumetric: in Cloudflare's report, an attack above 1 Tbps, 1 billion packets per second or 1 million requests per second.
- Threshold: a limit above which traffic is counted or blocked, such as the 1 Tbps cutoff for hyper-volumetric or the requests-per-minute value in a rate limiting rule.
The report also uses reflection and amplification: the attacker sends small queries with a forged source address to open servers, and the replies, many times larger, go to the victim.
How big and how long is a typical attack?
In H1 2026, 96.62% of network-layer attacks Cloudflare mitigated stayed under 500 Mbps and 90.60% ended in under 10 minutes. The median attack is short and small, but Cloudflare adds that "small" is relative and that most internet properties could not withstand even those attacks.
Cloudflare's own yardsticks in the report: a 100 Mbps attack is enough to overwhelm a server or website, and a 100 Gbps attack can knock most unprotected data centers offline. The largest attacks can be over in seconds, and Cloudflare says there is no practical window for human intervention.
Want to see this handled in real time?
Open the Security Lab and watch protected versus unprotected servers respond to the same simulated traffic pattern side by side.
Open the Security Lab Get your free server checkCan a small attack still take a small server offline?
Yes. Cloudflare's report says 100 Mbps is enough to overwhelm a server or website, far below the 500 Mbps line that 96.62% of attacks stay under. Most attacks Cloudflare calls small are still larger than a single unprotected VPS is built to absorb.
In its Q3 2026 report, Cloudflare describes short-burst, mid-range, high-count attacks as the signature of DDoS-for-hire "booter" services, aimed mostly at computer software, gambling and information technology companies. For HTTP floods, our reasoning (not a Cloudflare figure) is that a modest request rate against an expensive endpoint, such as a login page or a search box, can exhaust a small server without any large bandwidth.
What does a CDN protect, and what does it leave open?
A CDN or reverse proxy absorbs attacks aimed at the hostnames it proxies, because that traffic is filtered before it reaches your server. It does not protect a server whose real IP can be reached directly, ports it does not proxy, or an expensive endpoint that receives legitimate-looking requests.
| Threat | Does the CDN stop it? | What you add |
|---|---|---|
| Network-layer flood at your proxied site | Yes, at the edge. Cloudflare's docs list unmetered DDoS protection for layers 3 to 7 on all plans, including Free | Nothing extra for volume |
| Flood sent straight to the origin IP | No, it never passes the proxy | Firewall that accepts 80 and 443 only from Cloudflare, Authenticated Origin Pulls |
| Traffic to ports Cloudflare does not proxy (SSH, mail, databases) | No. By default Cloudflare proxies only listed HTTP and HTTPS ports; proxying any TCP or UDP port needs Spectrum, Enterprise only per the docs | Close those ports or restrict them in your firewall |
| Real-looking requests to a costly endpoint | Only in part; app-specific limits are yours to set | Rate limiting, fail2ban on logs, nginx limits |
Why the origin IP must not be reachable around the CDN: the protection runs only on traffic that passes through the proxy. Cloudflare's own IP address documentation says that someone who finds the origin IP, for example in historical DNS records or mail server configuration, can bypass Cloudflare's protections, and it recommends blocking traffic that does not come from Cloudflare's published ranges. Our guide Is your origin IP exposed behind Cloudflare? shows how to test this with curl and how to lock the origin down. For choosing protection at a small-business budget, see DDoS protection for a small business.
Fail2ban does not stop network-layer floods, because they saturate the link before any request reaches a log. It can ban clients that repeat abusive patterns the application does log, which is the layer a CDN leaves to you.
Scope: this page covers sites that can be put behind a proxy. It does not cover game servers, VoIP or other non-HTTP services, which need a different kind of protection. For a case where an outage had nothing to do with DDoS, see what the Yandex data center strikes mean for resilience.
Has anything changed since the H1 report?
Yes. Cloudflare's Q3 2026 report (29 October 2026) counts 18.2 million network-layer attacks, attacks above 1 Tbps down from 805 to 251, and 96% of attacks ending in under 10 minutes. The H1 numbers are a snapshot, not a fixed trend.
- 98% of attacks stayed under 1 Gbps, which Cloudflare still describes as more than enough to overwhelm a server or website.
- CLDAP floods fell to 0.05% of attacks, while DNS amplification rose 215% to 3.43%.
- Cloudflare says the drop in the largest attacks coincides with law enforcement action in early 2026 against four IoT botnets (Aisuru, KimWolf, JackSkid and Mossad), and that new variants keep appearing.
Sources and how this page was checked
On 13 November 2026 we checked each figure against the text of Cloudflare's H1 2026 DDoS Threat Report (25th edition, Cloudforce One, published 11 August 2026). The blog page loads its body with scripts, so we read the post text from Cloudflare's own RSS feed for the DDoS tag. We also read the Q4 2025 report, the Q3 2026 report, the 500 Tbps capacity post and Cloudflare's documentation on DDoS protection, network ports and IP addresses. A summary on dbugs (24 August 2026) repeats the same H1 figures, so it is not independent confirmation.
What we could not check: Cloudflare Radar report pages refused automated access (HTTP 403), so we do not cite them as read, and we did not use numbers that appear only in chart images. We ran no tests for this page. The curl check in the quick win comes from our origin IP guide, which we ran on 9 November 2026.
Corrections made on 13 November 2026: the 31.4 Tbps attack belongs to the Q4 2025 report, not the H1 2026 one; we removed the month "December 2025", the claim that the largest attacks target only large organizations, a list of "realistic scenarios" and a set of request-rate figures that Cloudflare's reports do not state, and the description of a secondary summary as independent analysis.
Frequently asked questions
What was the largest DDoS attack Cloudflare has mitigated?
Cloudflare reported a 31.4 Tbps attack lasting 35 seconds in its Q4 2025 report (5 February 2026), attributed to the Aisuru-Kimwolf botnet. It is the largest attack we found in Cloudflare's reports up to its Q3 2026 edition.
How many DDoS attacks did Cloudflare mitigate in H1 2026?
Cloudflare mitigated 23.2 million network-layer DDoS attacks and 29.64 trillion HTTP DDoS requests in the first half of 2026, about 5,343 network-layer attacks per hour or 128,000 per day (H1 2026 report, 11 August 2026).
Does a record-breaking terabit-scale attack mean small servers are at higher risk?
Not directly. Cloudflare's H1 2026 data shows 96.62% of network-layer attacks stayed under 500 Mbps and 90.60% ended in under 10 minutes. But Cloudflare also says 100 Mbps can overwhelm a server, so small attacks still matter for an unprotected site.
What size of DDoS attack can take down a small business server?
According to Cloudflare's H1 2026 report, a 100 Mbps attack is enough to overwhelm a server or website. A small VPS does not need a terabit flood to go offline, and Cloudflare's report does not give a single size that applies to every server.
What is the difference between a network-layer and an HTTP DDoS attack?
A network-layer attack floods the network or transport layer (layers 3 and 4) with packets, and Cloudflare counts it in attacks, Tbps or packets per second. An HTTP DDoS attack floods the web application with requests that look legitimate, and Cloudflare counts it in requests.
Is a CDN or proxy enough DDoS protection for a small business?
For volume attacks on a proxied site, a CDN absorbs most of the load. It does not help if your origin IP is reachable directly, for ports it does not proxy, or for costly endpoints, so rate limiting and a firewall that only accepts Cloudflare on ports 80 and 443 are still needed.
What does hyper-volumetric DDoS mean?
In Cloudflare's report, hyper-volumetric means an attack above 1 Tbps, 1 billion packets per second or 1 million requests per second. Cloudflare counted 935 network-layer attacks above 1 Tbps in H1 2026.
Is Cloudflare DDoS protection free?
Cloudflare's documentation says standard, unmetered DDoS protection is available on all plans, including Free, for traffic that goes through Cloudflare. Check the current plan comparison in the docs, because adaptive rules and overrides differ by plan.
Can attackers bypass Cloudflare if they find my server IP?
Yes, if the server accepts connections from anyone. Traffic sent straight to the origin IP never passes Cloudflare's filtering, so allow ports 80 and 443 only from Cloudflare's published IP ranges.
Not sure where your server stands?
Get a free, read-only security check, or talk to a security engineer about managed protection.
Get your free server check Talk to a security engineer