Zero-day exploit
A zero-day exploit is an attack that uses a vulnerability the software vendor does not yet know about, so no patch exists yet. Rare in practice for small business servers compared to n-day exploits.
Why patching alone cannot stop this category
By definition, no patch exists yet for a zero-day vulnerability, since the vendor does not know about it. This is exactly why layered defenses such as a WAF, intrusion prevention, and least-privilege configuration matter even on a fully patched server.
What actually reduces the risk
Reducing the attack surface, running services with minimal privileges, and having monitoring in place to detect unusual behavior quickly all help limit the damage from a zero-day, even though none of them can prevent the vulnerability from existing in the first place.
For how patching fits into a layered defense, see our server patch management guide.
Shrinking what a zero-day can reach
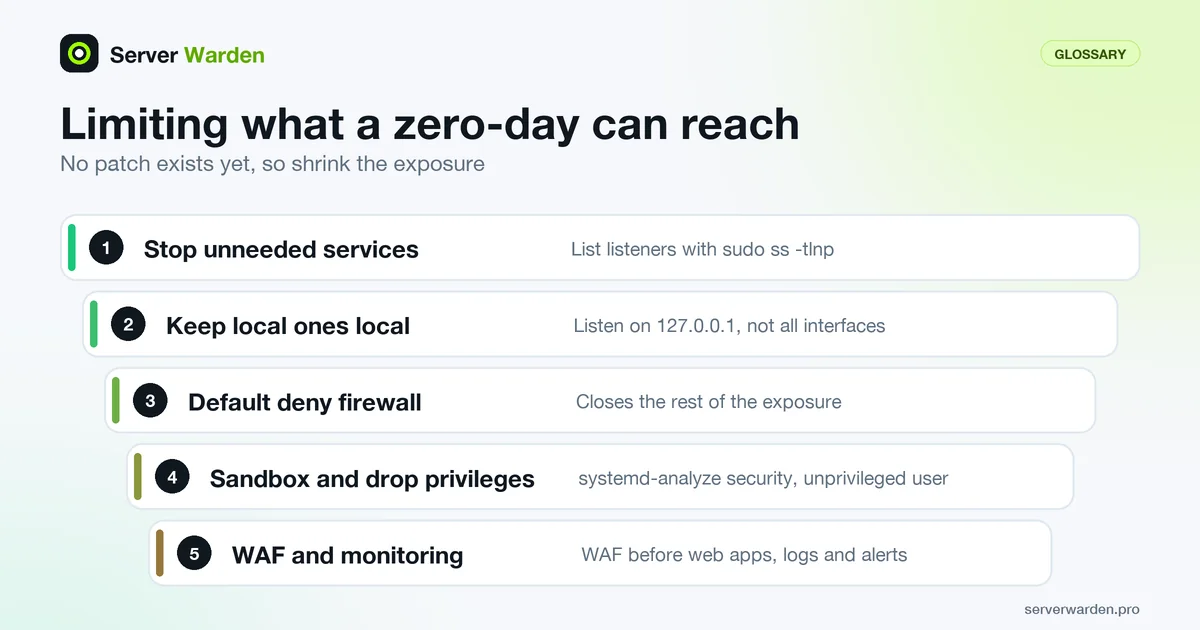
NIST defines a zero-day attack as one that exploits a previously unknown vulnerability. You cannot patch what nobody has found, but you can decide how much of your server such a bug would expose. Two commands give a quick picture:
sudo ss -tlnp
systemd-analyze security nginx.service
The first lists listening TCP sockets with the process behind each one (-t TCP, -l listening, -n numeric, -p processes). Every service you do not need should be stopped, and anything meant only for local use should listen on 127.0.0.1 instead of all interfaces. A default deny firewall, covered in the firewall guide, closes the rest.
The second gives a service an exposure score between 0.0 and 10.0, where higher means weaker sandboxing. The systemd-analyze documentation notes that it only measures systemd's own per-service restrictions, not protections built into the service. Tightening those settings, running as an unprivileged user (see the least privilege audit) and keeping a WAF in front of web applications limits what a successful exploit can do next.
From advisory to patch: handling the gap
Often the first sign of a zero-day is a vendor or researcher advisory that arrives before a fix does. NIST's SP 800-40 Rev. 4 calls the response emergency mitigation: a temporary measure, such as deactivating the affected functionality or isolating the system, applied before a patch exists. It also says to plan the exit: once a patch is available, deploy it and remove the mitigation, with schedules set and enforced for both steps.
CISA's KEV criteria use the same vocabulary. A mitigation is a temporary solution, a workaround is a manual change that protects the product until a formal patch arrives, and CISA recommends using a workaround over leaving a product vulnerable. The NGINX Rift write-up shows the pattern in practice: a configuration stopgap is useful, but it does not replace the real fix.
The moment a patch ships, the bug becomes an n-day and the race shifts to how fast you install it. Until then, rely on logs and alerts to notice odd behavior early, as described in the monitoring guide, and keep the incident response steps within reach.
Related terms: N-day exploit, Patch management, Intrusion prevention, WAF, CVSS, CISA KEV catalog.
Frequently asked questions
How common are zero-day attacks against small businesses specifically?
Less common than exploits against already-known, unpatched vulnerabilities, since zero-days are comparatively rare and often reserved for higher-value targets, but they are not impossible.
Does a fully patched server mean I am safe from zero-days?
No, since a zero-day exploit targets a vulnerability nobody has patched yet, by definition. Patching protects against known issues, which is still the vast majority of real-world attacks.
What happens once a zero-day becomes publicly known?
It typically becomes an n-day exploit, meaning a patch usually follows soon after, and the priority shifts to applying that patch as quickly as possible before attackers who reverse-engineer it can act.
Where should I watch for zero-day advisories that affect my server?
Follow the security advisories of the vendors and distributions behind the software you actually run, and check the CISA Known Exploited Vulnerabilities catalog. KEV lists vulnerabilities with an assigned CVE, reliable evidence of active exploitation and a clear remediation action.
Is every vulnerability on the CISA KEV catalog a zero-day?
Not by definition. KEV requires a clear remediation action, such as a vendor update, so a listed entry is something you can act on. A flaw that was exploited before disclosure may have been a zero-day earlier, but once listed it is handled like an n-day.
Want to see where your own server stands?
Run the free, read-only server check, or open the Security Lab and watch the detect, contain, recover, verify loop in action.
Get your free server checkOpen the Security Lab